WhiteTie · Security

Miguel Ángel Hernández

Lead Security Engineer

Twenty years making software and the cloud harder to break: from penetration testing and threat modelling to building secure SDLCs and leading security teams.

Remote · Alicante, Spain

WhiteTie logo: a white tie engraved with circuit traces and binary code
Scroll
Security Engineering◆AI Security◆SDLC Security◆ Cloud Security◆Penetration Testing◆Audit & Compliance◆ Leadership◆Mentoring◆Threat Modelling◆Kubernetes◆
0+

years in information security, since 2006

0

industry certifications: OSCP, CKA, CISM, CISA…

0

conference talks & master classes across Europe and the US

0B+

lifetime users served by the product I secure today

Miguel Ángel Hernández speaking at Blue Code 2026, wearing his signature white tie
Blue Code · Master Class, 2026

Profile

A security engineer who still enjoys getting his hands dirty.


I like to see myself as a seasoned security professional with a broad range of skills in Security Engineering Management and Leading, Security Operations, Security Consultancy, Penetration Testing and Security Architecture.

My experience ranges from hands-on penetration testing of on-prem and cloud applications to discovery, gap analysis and defining architecture requirements for cloud services. I am an individual contributor and a team player with an eye for detail and a strong work ethic.

I am passionate about security and constantly strive to enhance my knowledge, by attending and presenting at industry-leading security conferences and by mentoring and doing knowledge transfer with my team members.

Languages

  • Spanish / Castilian
  • English
  • Catalan / Valencian

Expertise

Four disciplines, one goal: secure by design.

01

Security Engineering & Leadership

Leading security programmes, embedding controls into the SDLC, DevSecOps, threat modelling (OWASP, AWS) and mentoring engineers to raise the bar.
  • SSDLC
  • OWASP SAMM
  • ASVS
  • DevSecOps
02

Offensive Security

Web, API, network and infrastructure penetration testing since 2013. Research into new attack vectors and turning findings into real fixes.

  • OSCP
  • SANS AWAPT
  • Burp Suite
  • Metasploit
03

Cloud & Cloud-Native

Security architecture for AWS, Azure and IBM Cloud; Kubernetes maturity models, Flux CD reference architecture, distroless and AI security.

  • CKA
  • Kubernetes
  • AWS
  • Azure
04

Governance & Compliance

ISO 27001 implementation and audit, risk analysis (ISO 27005), HIPAA readiness, policies and building incident response teams from scratch.

  • ISO 27001
  • CISA
  • CISM
  • HIPAA

Career

From research labs to a billion users.

Highlights of each role. Open any entry for the full detail.

  1. 2024Present

    Lead Security Engineer Smallpdf · Remote

    Leading security at the Swiss leader in document & PDF technology: a top-300 global website serving over a billion lifetime users in 24 languages.

    • New SDLC controls to detect and mitigate vulnerabilities in third-party and in-house code
    • Active role in the ISO 27001 certification and audit processes
    • Internal pentesting, research on new attack vectors and L7 / WAF controls
    Full detail
    • Lead the efforts to ensure company software and systems are designed and implemented to the highest security standards
    • Perform technical security assessments, code reviews, vulnerability testing and advanced monitoring
    • Work closely with other engineers to design and build processes and guidelines to enhance security
    • Coordinate cybersecurity risk assessment and routine penetration testing
    • Partner with internal product teams to continuously improve overall product security
    • Develop technical solutions to help mitigate security vulnerabilities
    • Promote and advise on security and secure practices throughout the company
    • Collaborate with developers to integrate security best practices into development (DevSecOps)
    • Design, implement and maintain security controls for cloud applications using L7 tools (e.g. WAFs)
    • Develop and document security policies and procedures
  2. 20232024

    Principal Cloud Native Security Consultant ControlPlane · Remote

    Consultancy at a recognised leader in Kubernetes and cloud security research, working for some of the most important companies worldwide.

    • Co-authored a Kubernetes & Containers Maturity Model
    • Contributed to the first ever Reference Architecture for Flux CD
    • Helped create an AI Security Reference Architecture for Helix.ml
    Full detail
    • Managed an internal project for the adoption of a DAST tool
    • Internal penetration testing
    • Research on distroless security
    • Led Invitation to Tender responses and engaged with partners on joint submissions
  3. 20222023

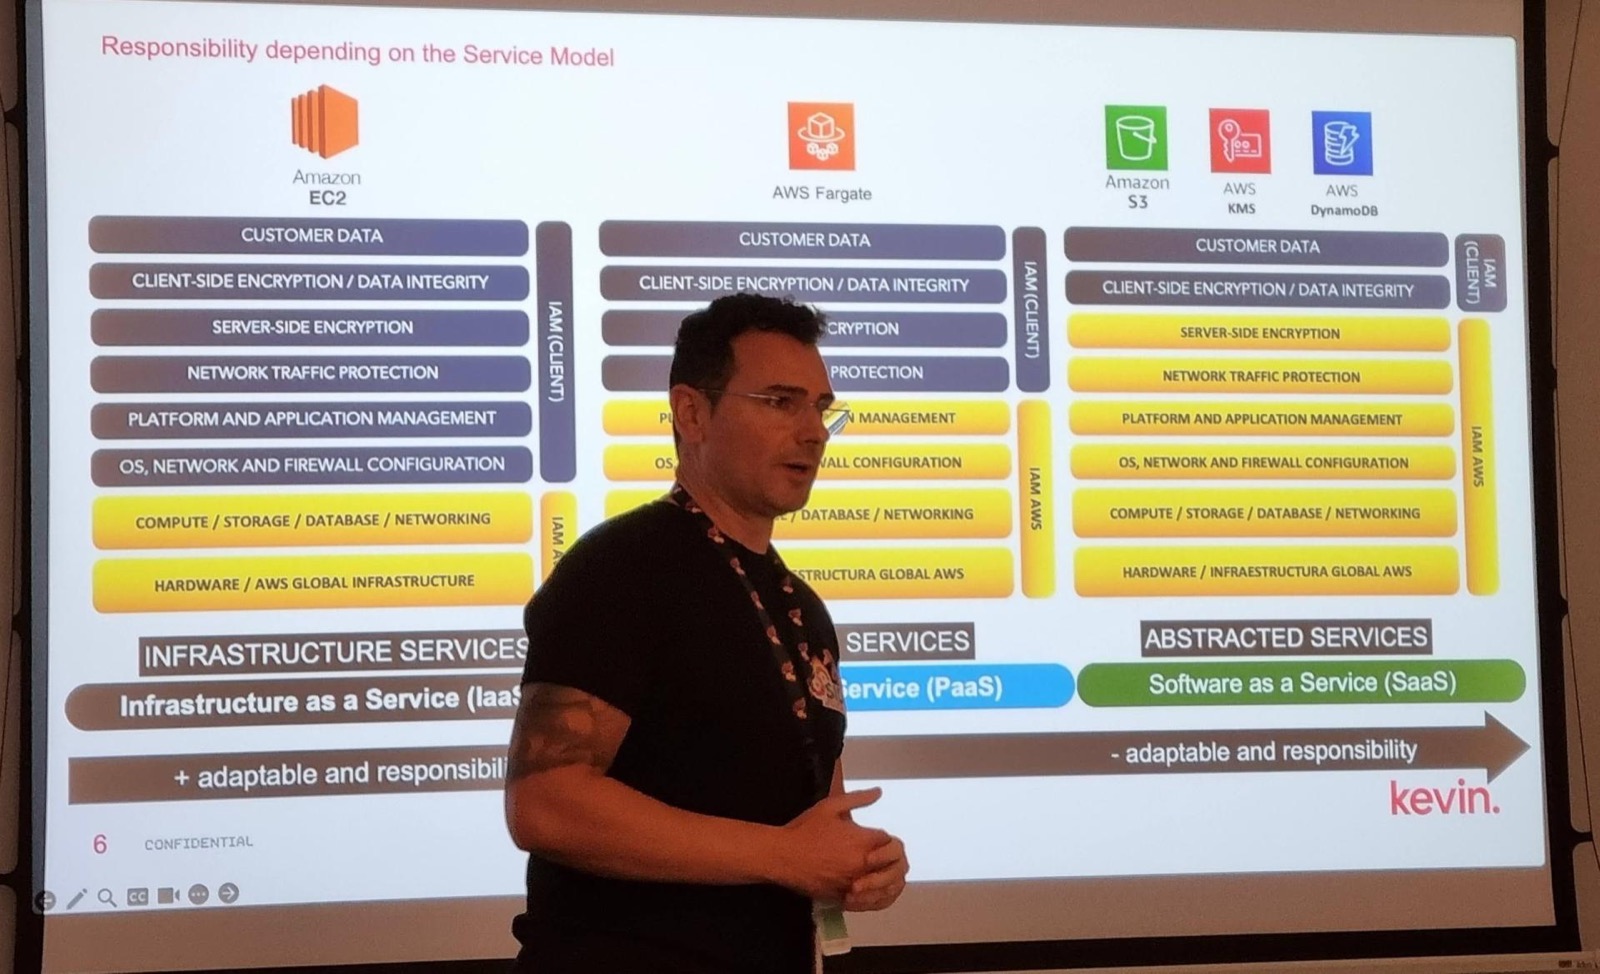
    Senior Security Engineer Kevin. · Remote

    Built the application security function of a young fintech from zero, aligned with OWASP SAMM.

    • Designed a Threat Modelling methodology for a Kubernetes-based agile environment
    • Security Requirements process based on OWASP ASVS
    • Automated AWS IAM analysis to detect unused or stale permissions
    Full detail
    • Security requirements reviews and threat modelling for new Kubernetes-based applications
    • Architecture analysis in early phases to embed security from conception
    • Led projects from zero to full implementation, creating an SSDLC according to OWASP SAMM
    • Aligned security projects with business strategy to guide the security roadmap
    • Penetration testing of internal applications; triage of SAST and SCA findings
    • Mentored application security team members
    • Led an IAST implementation project
  4. 20212022

    Cloud Security Architect IBM · Remote

    Security architect for Watson Health and IBM Cloud during the transition of offerings from IBM Cloud to Microsoft Azure.

    • Security Architecture Reviews and exploit-driven validation of weak points
    • Framework turning HIPAA and internal standards into technical requirements
    • PSIRT focal for Key Protect and a flagship Watson Health offering
    Full detail
    • Azure services exploration and delta analysis versus IBM Cloud for future migrations
    • Project management of a HIPAA Readiness implementation for Key Protect
    • Public Cloud exceptions raising, follow-up and management
    • Internal process improvements and documentation
    • Mentoring security engineers on assessments and promising attack avenues
  5. 20162021

    Senior Security Engineer / Penetration Tester IBM · Dublin / Remote

    Security Operations in the Watson Health business unit.

    • Penetration testing of cloud and on-prem apps (UI and API) with the OWASP Testing Guide v4
    • Persistent Security Testing: automated tests for early vulnerability detection
    • Security process aligned with dev and QA, including audit-ready records
    Full detail
    • Tooling: Burp Suite, sslscan, Metasploit, ZAP, nmap, kube-hunter, kube-linter, Python, W3AF, Skipfish, Nikto, AppScan
    • PSIRT focal: investigated Product Vulnerability Records across offerings
    • Verified, assessed and supported fixing of vulnerabilities reported by clients
  6. 20132016

    IT Security Consultant / Penetration Tester Sopra Steria · Alicante

    Pentest team coordination for clients such as EUIPO, AXA, GDF-Suez and Mutua Universal.

    • Web, API, network and infrastructure penetration testing
    • Coordinated and managed the penetration testing team
    • Security awareness and training to skill up teammates
    Full detail
    • Tooling: Burp Suite, ZAP, Metasploit, SoapUI, Hydra, Medusa, Skipfish, OpenVAS, Nessus, DirBuster, Nmap, sqlmap
    • Vulnerability risk calculation using CVSS
    • Presales technical support, Calls for Tenders and Calls for Information
    • Standards: ISO 27001, ISO 27034, OpenSAMM, OWASP Testing Guide, ASVS, NIST 800-64, PCI-DSS, PA-DSS, LOPD
  7. 20082013

    Information Security Consultant Firma-e · Murcia

    ISMS implementation and audit, risk management and incident response.

    • ISO 27001 ISMS implementation, certification and internal audits
    • Built a Computer Security Incident Response Team from scratch
    • ISMS Responsible at a Directorate General of IT & Communications
    Full detail
    • Risk analysis with an ISO 27005 compliant methodology and treatment planning
    • Documentation control and periodic review of procedures, norms and policies
    • Non-conformities management; business continuity based on BS 25999-1
    • Mentor and instructor of security awareness training; incident response coordination
    • ITIL Practitioner
  8. 20062008

    Security Researcher University of Murcia

    Research while completing my Degree and Master's: identity and intrusion detection.

    • CTNET: documentation framework for a new Regional CSIRT for Murcia
    • IDS/IPS research to improve detection in Snort and Prelude
    • EcoSpace: distributed identification system based on OpenID
    Full detail
    • Web Services semantic annotation (SA-WSDL) and Abstract BPEL process designs
    • Web Services development in Java; shared folder synchronisation

On stage

A security evangelist.

Selected as a speaker at some of the most important security and testing conferences.
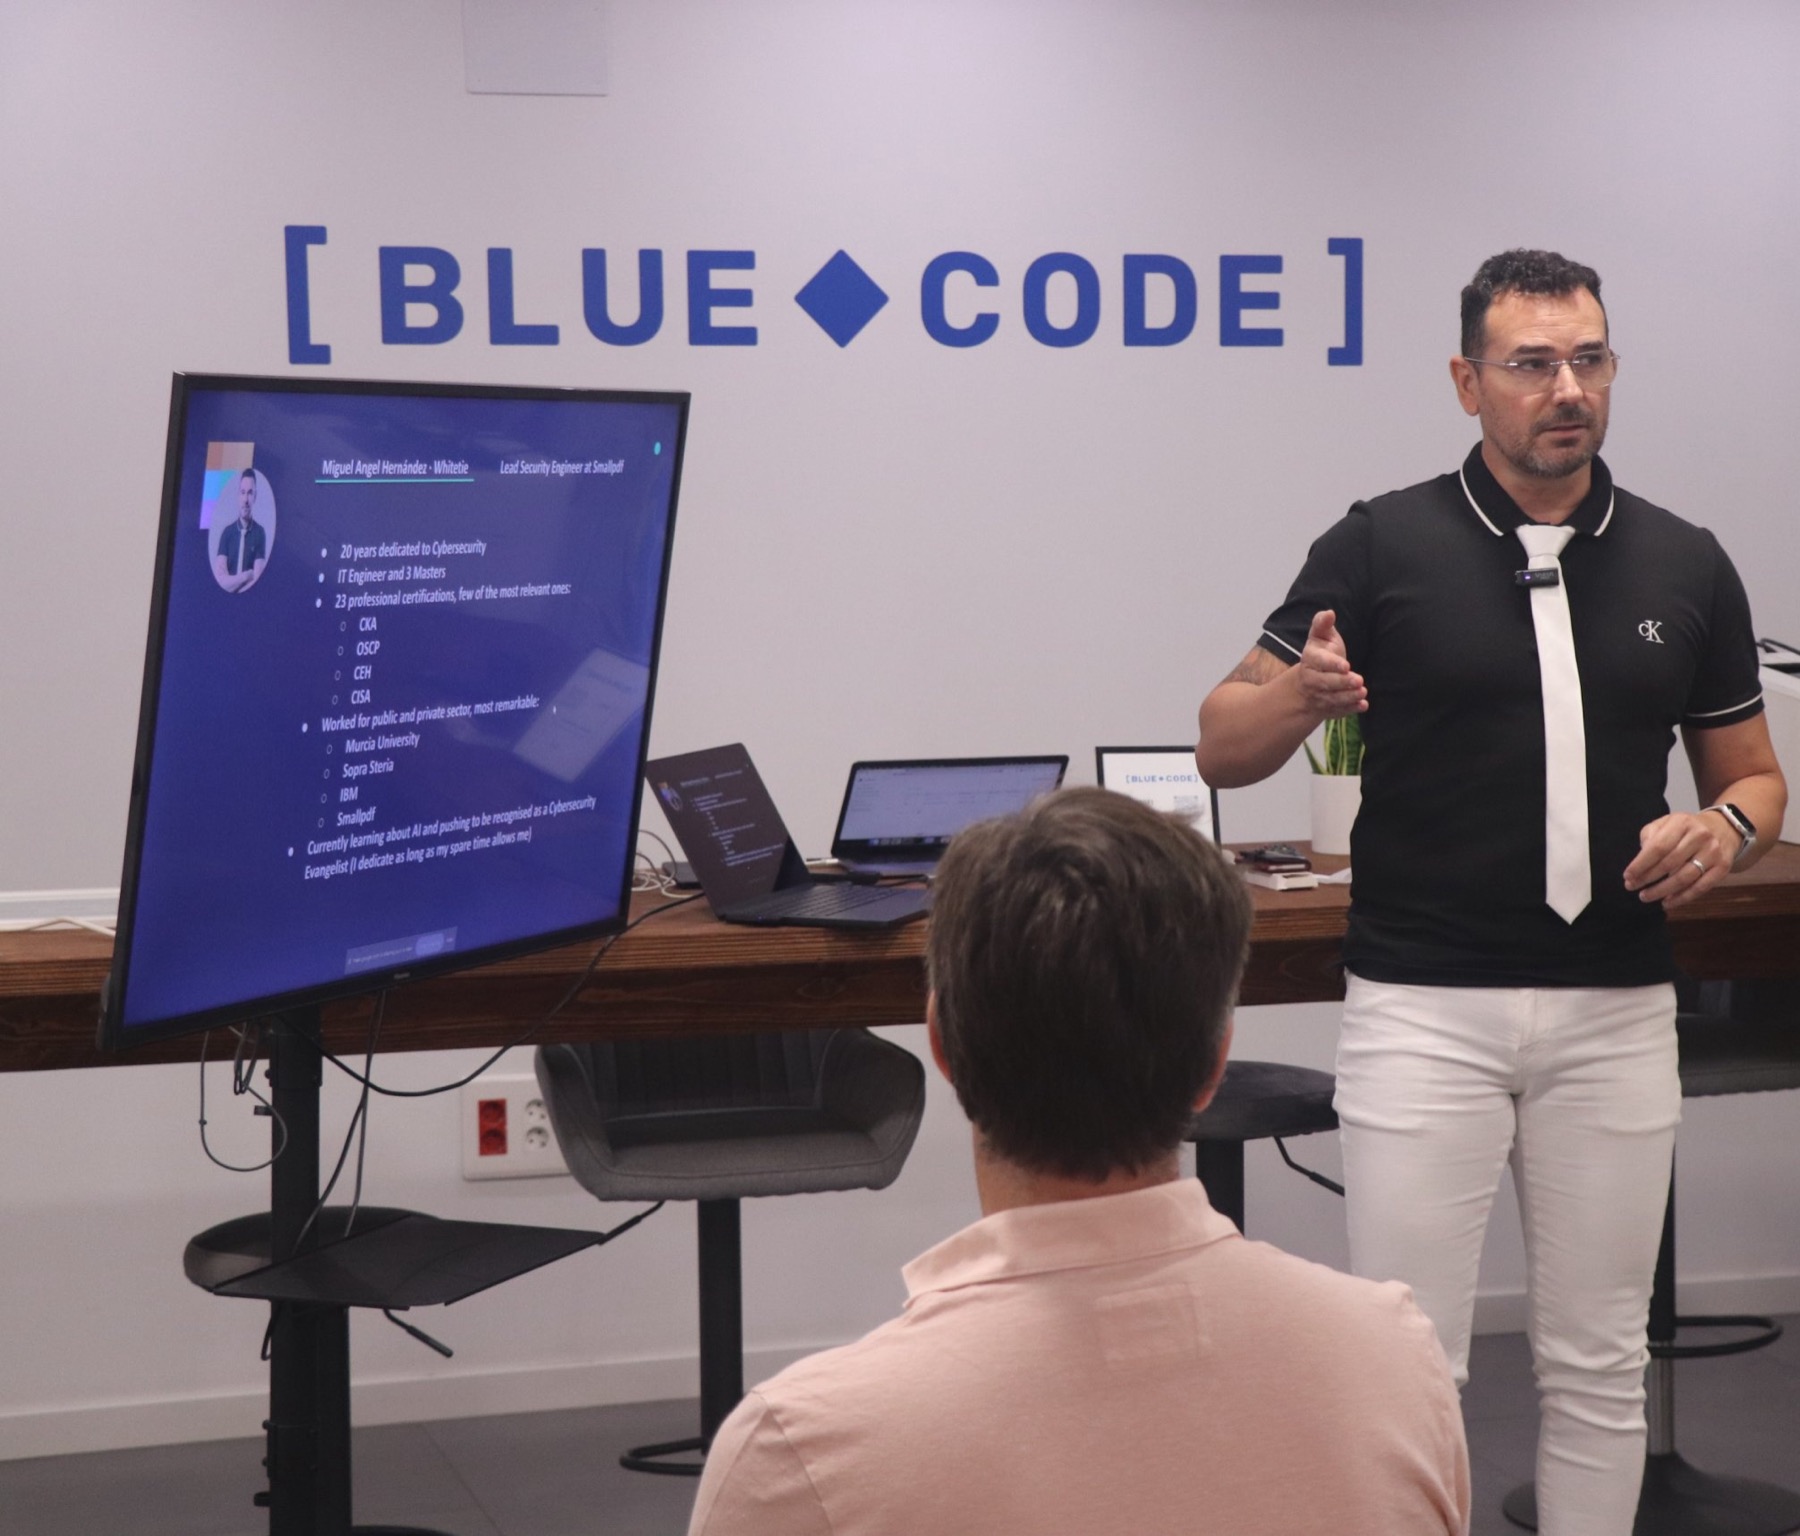
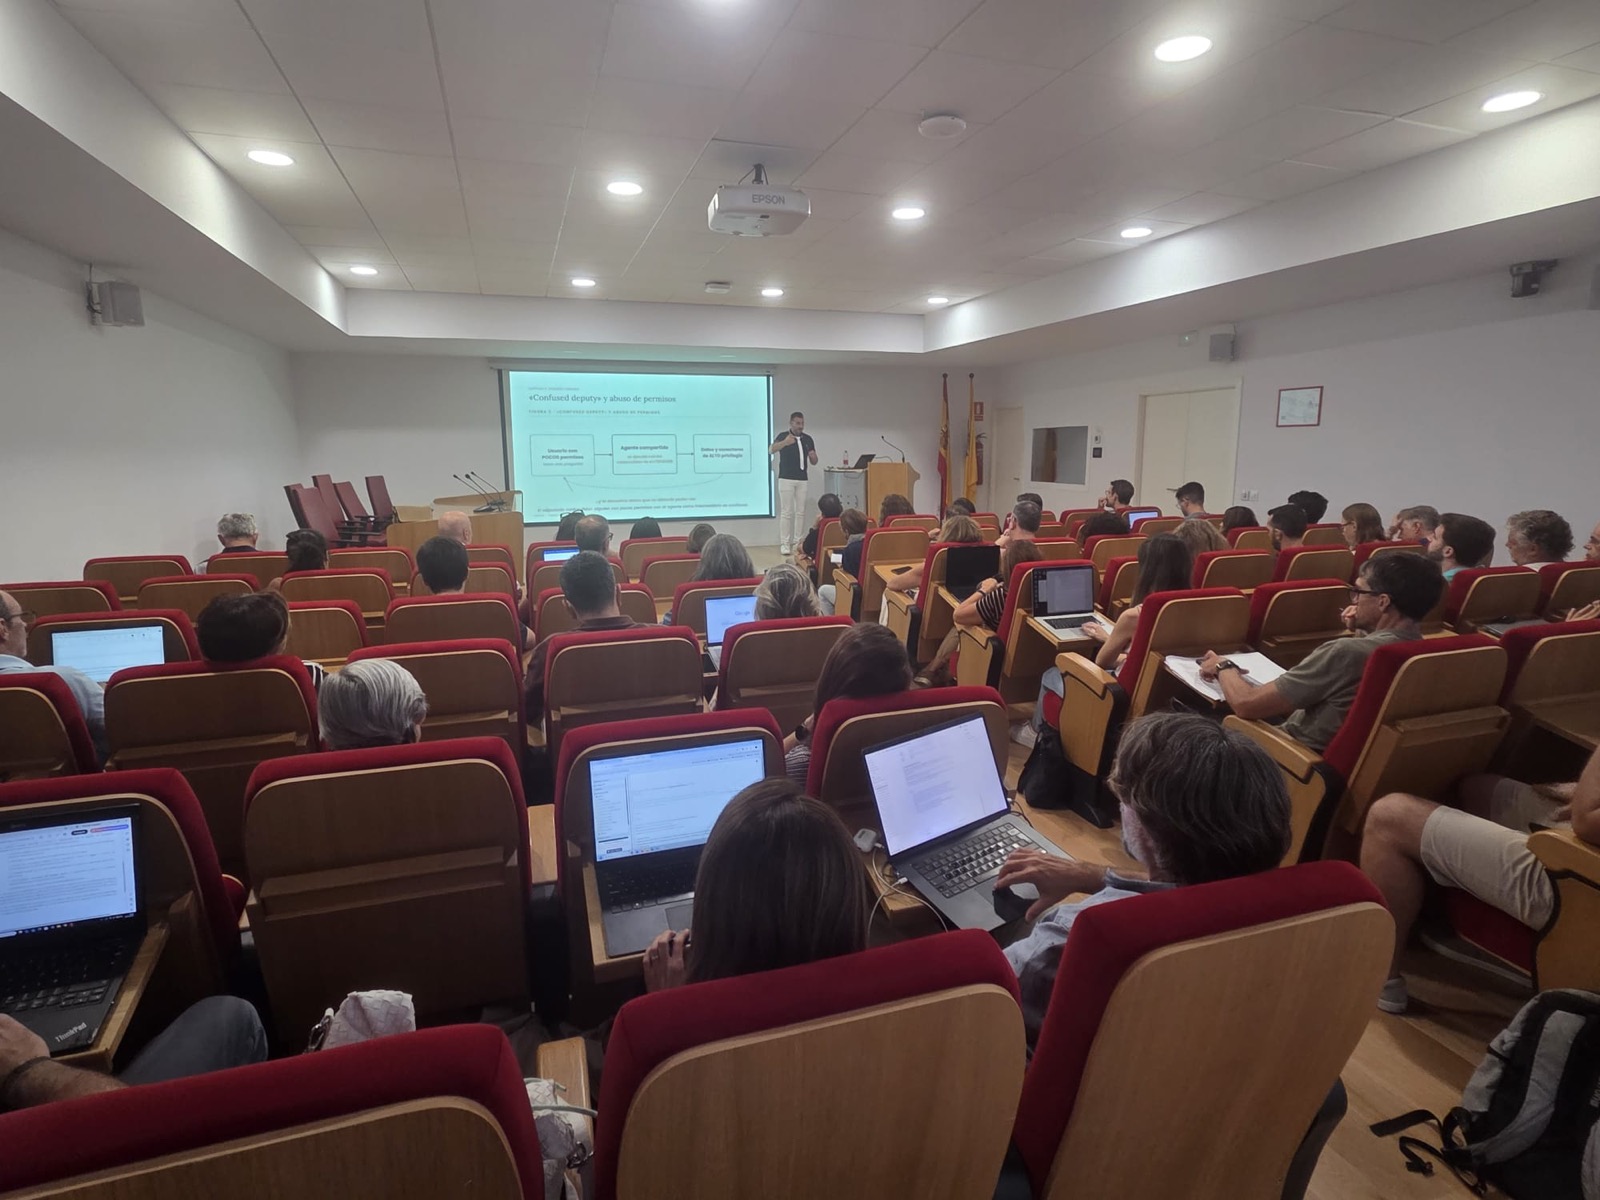
Speaking at Blue Code, 2026
Blue Code Master Class · 2026
Master Class at the University of Cádiz, 2026
University of Cádiz Master Class · 2026
Blue Code session, 2026
Blue Code Live demo · 2026
Talk at BSides Krakow, 2023
BSides Krakow 2023
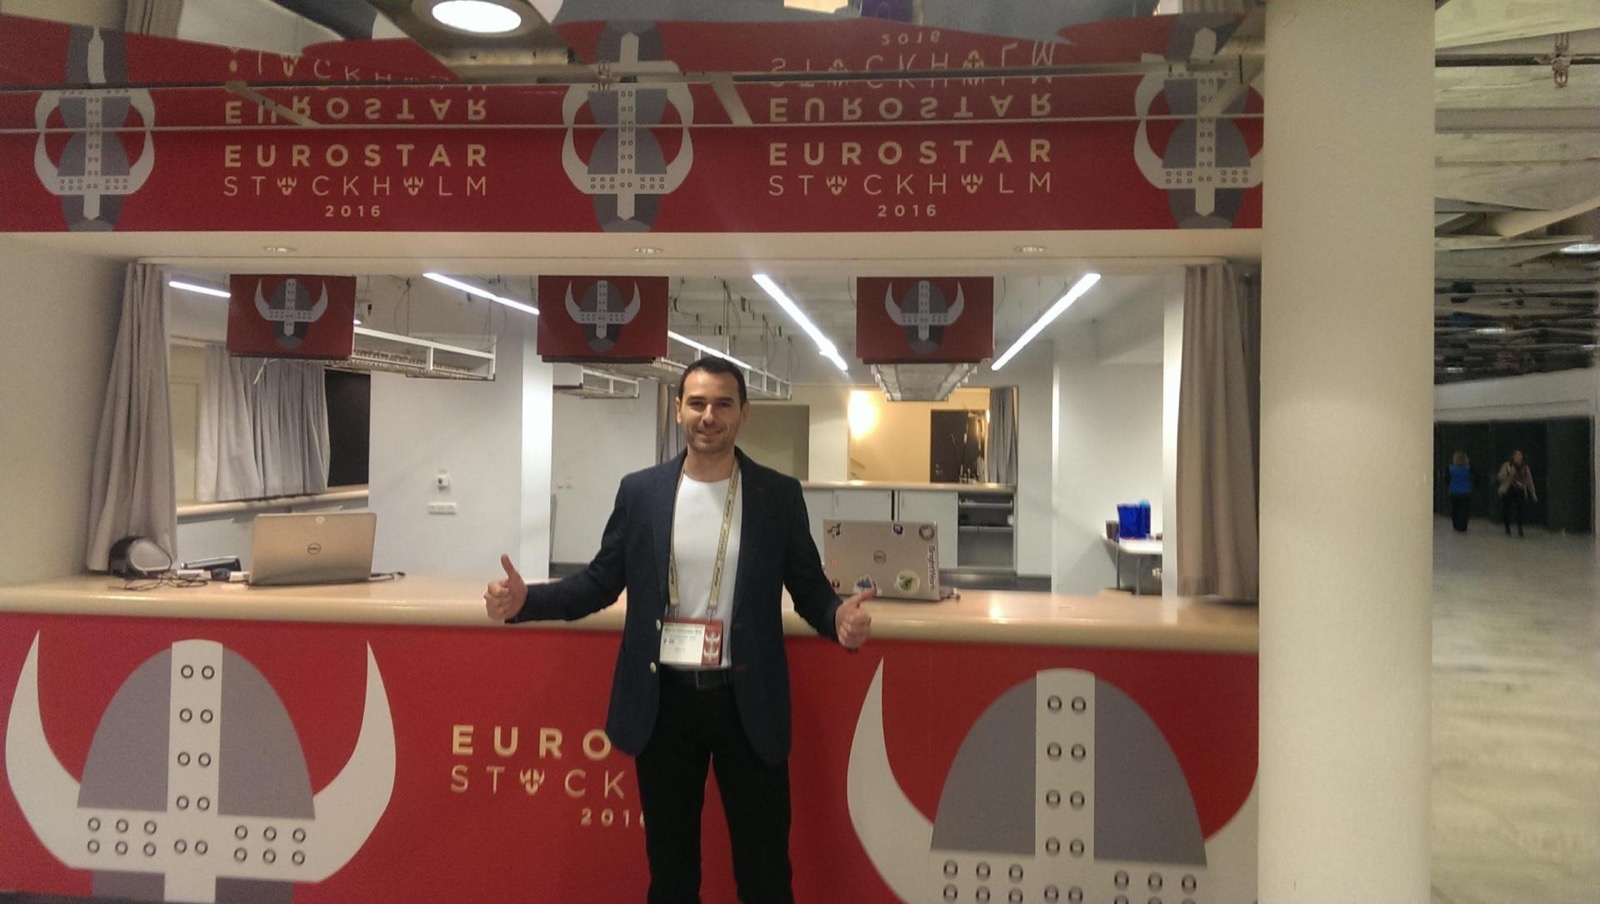
At EuroSTAR Stockholm, 2016
EuroSTAR Stockholm · 2016
Master Class at Test Academy Barcelona, 2016
Test Academy Barcelona · 2016
Talk at After Test Madrid, 2016
After Test Madrid · 2016
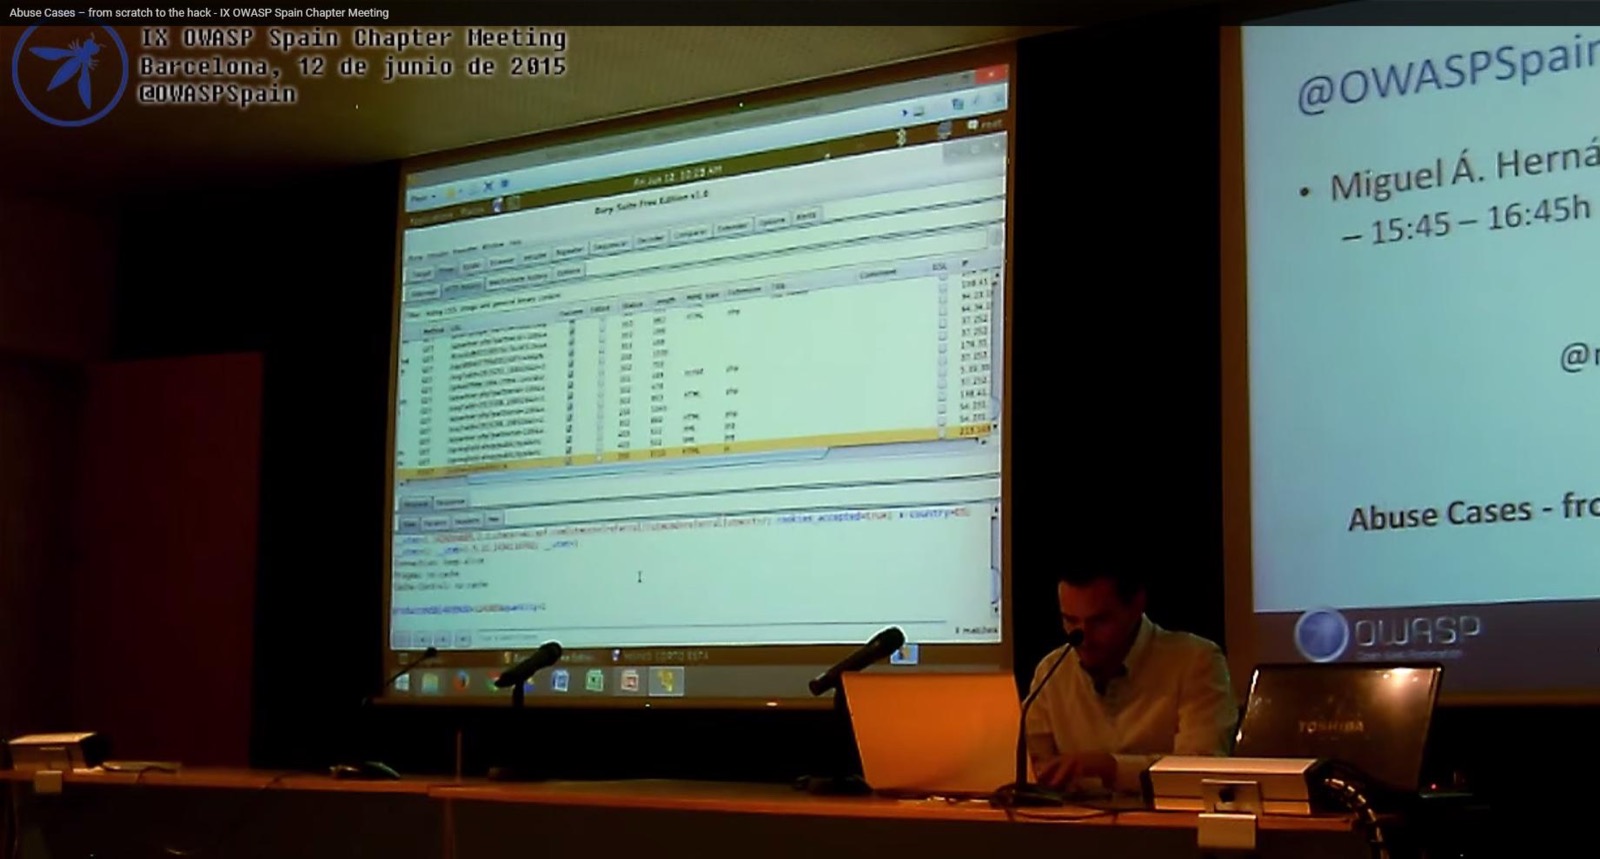
Abuse Cases talk at OWASP Spain chapter, Barcelona 2015
OWASP Spain Barcelona · 2015
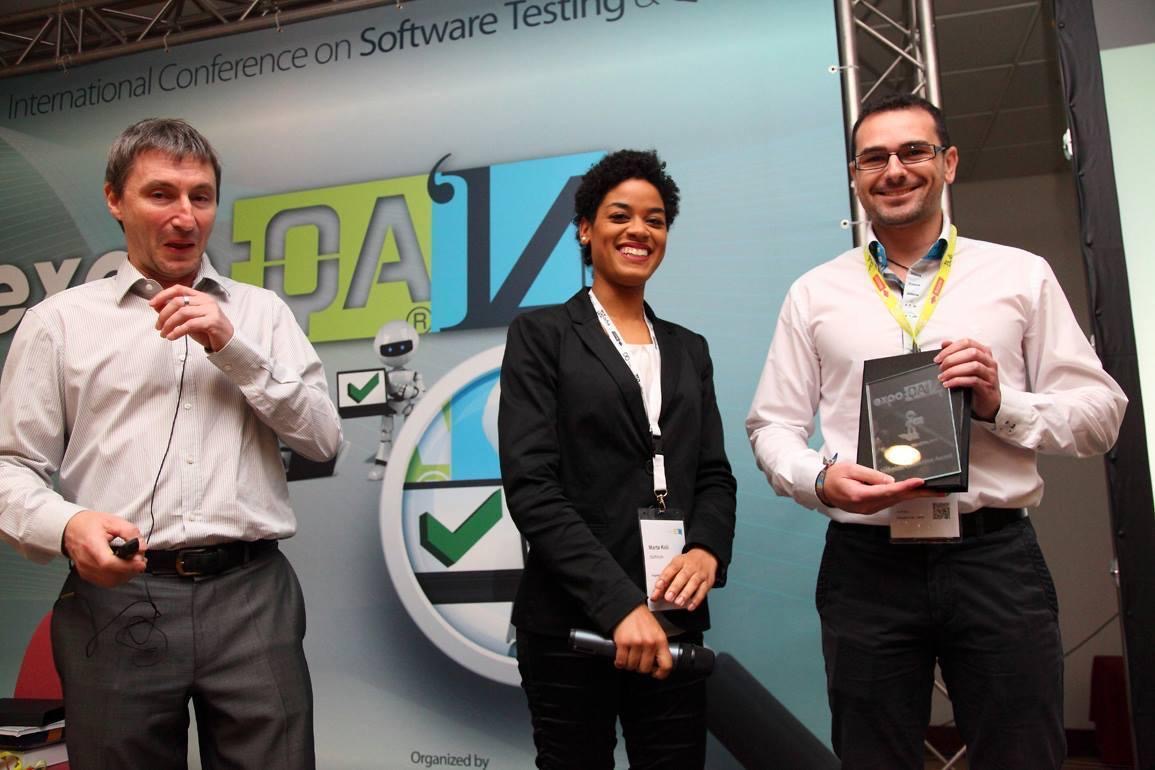
Receiving the Technical Committee Award at Expo:QA 2014
Expo:QA Technical Committee Award · 2014
  • 2026Cádiz University Master Class
  • 2026DevOps Meetup Zurich
  • 2026Blue Code Master Class
  • 2023BSides Krakow
  • 2023BalCCon Novi Sad
  • 2023Severo Ochoa Master Class
  • 2023BATOY Cybersecurity Journey
  • 2018ConTEST New York
  • 2018Test Automation Day
  • 2016Test Academy Barcelona Master Class
  • 2016After Test Madrid
  • 2016EuroSTAR
  • 2015OWASP
  • 2015CyberCamp
  • 2014Expo:QA
  • 2014–15VLC-Testing

Credentials

Twenty-three certifications, earned over time.

A selection of the most relevant ones.

  • CKACertified Kubernetes Administrator
  • AWS CCPAWS Certified Cloud Practitioner
  • SC-900Microsoft Security, Compliance & Identity Fundamentals
  • IBMC-SAIBM Cloud Security Architect
  • AWAPTAdvanced Web Application Penetration Tester · SANS
  • OSCPOffensive Security Certified Professional
  • SPSESecurityTube Python Scripting Expert
  • CEHCertified Ethical Hacker · EC-Council
  • ISTQBISTQB Foundations
  • ITILITIL Foundations v3
  • CISMCertified Information Security Manager · ISACA
  • ISO 27001 LAIRCA Lead Auditor · SGS
  • CISACertified Information Systems Auditor · ISACA

Honours & awards

  • Strong Performer AwardIBM
  • Hero AwardIBM
  • Manager’s Choice Award ×2IBM
  • Technical Committee Award, Expo:QA’14“Security Testing: Overcoming the Obstacles”
  • IEEE Best Paper Award“Event Driven Architecture for Intrusion Detection Systems Based on Patterns”
  • Bachelor Thesis with HonoursUniversity of Murcia

Education

  • Master in Business AdministrationUniversity of Murcia
  • Master in IT & Advanced TelecommunicationsUniversity of Murcia
  • Master in Pedagogical SkillsUniversity of Murcia
  • IT Superior Engineering DegreeUniversity of Murcia
Courses & badges
  • PSIRT Responder, IBM
  • Interskill: Coaching and Mentoring for Technical Specialists, IBM
  • Security Focal, IBM
  • Security and Privacy by Design Foundations, IBM
  • Think Like a Hacker, IBM
  • Beyond the Basics: Istio and IBM Cloud Kubernetes Service
  • Getting Started with Microservices with Istio and IBM Cloud Kubernetes Service
  • Docker Essentials: A Developer Introduction, IBM

Contact

Let’s talk security.

Leadership roles, consulting, talks or a good technical conversation: my inbox is open.

ingeniero.miguelruiz(at)gmail.com